All captchas
Auto check
auto_checkMost visitors do nothing: the check runs in the background, and only those it is unsure of get a puzzle.
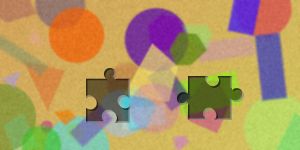

One more step: please solve this challenge.
Checking…WAU Captcha


Facts
- Media
- None: a box of about 300 × 64
- Answer
- Browser checks and behaviour, sent by the SDK
- Lifetime
- 2 minutes, answered once
- Behaviour check
- Yes, while it is on screen
What the person does
- Nothing, most of the time. Once the box comes into view it says “Checking…”, while the browser solves a proof of work and the SDK looks at the browser and at how the pointer moves on the page.
- After a second and a half, or a little more, the box turns into “Verified” and the form has its token.
- A visitor the check is unsure of is never told why: “One more step: please solve this challenge.” and a challenge of the fallback type appear in the same place.
Why it is hard for bots
- Every signal inside the browser can be faked by a determined bot, so a pass leans on three things such a bot cannot fake from inside it: a puzzle this browser solved on your site before (the clearance, kept up to 7 days and good for at most 6 automatic passes an hour and 24 a day), an address that does not belong to a cloud or hosting provider, and caps per address.
- Plain HTTP scripts: an answer needs a proof of work, behaviour recorded for over a second and the headers of a real browser, and a User-Agent of an HTTP library or an automation tool is refused outright.
- Headless browsers that do not hide themselves: navigator.webdriver, a HeadlessChrome User-Agent, a window without an outer size, WebGL drawn in software (SwiftShader, llvmpipe), or notifications denied while the browser says it would ask.
- Stealth plugins that patch browser functions: a navigator.webdriver or a Function.prototype.toString that is not native, or a User-Agent or language that differs from the one in the request's headers.
- Every pass costs the browser a proof of work of 18 bits, about 8 times that of the other types, and one address gets at most 30 automatic passes an hour, 5 of them without a clearance; after that it sees the fallback.
- The judgement has no randomness: the same browser asking again is judged the same way, so trying again gains a script nothing but more work.
Strict or balanced
- Strict: a visitor passes automatically only after solving one puzzle on your site in this browser. It is the strongest: the first visit always shows a puzzle.
- Balanced: a first visit from a home or mobile address may also pass on its signals alone, up to 5 an hour per address, with the reason first_visit.
- WAU Captcha runs in balanced mode.
What your backend can check
- /siteverify says in behavior.reasons how an automatic pass was earned: cleared, by a browser that solved a puzzle on your site before, or first_visit, on its signals alone.
- Refuse first_visit for sign-ups, logins and payments, and show a puzzle there instead: balanced mode is then as strong as strict where it matters, and costs nothing on your other forms.
What it does not stop
- A determined attacker can solve puzzles, or pay people to, and so earn clearances: each one buys at most 6 automatic passes an hour and 24 a day, in the browser that solved it.
- In balanced mode, a bot behind home or mobile addresses, such as residential proxies, gets up to 5 first visits an hour per address. Refusing first_visit is what stops it where it matters.
- Cloudflare Turnstile and Google reCAPTCHA judge with far more data, such as what they see of an address across millions of websites; WAU Captcha sees your own traffic only.
What the SDK sends and stores
- The names of the checks that tripped, such as outer_zero or software_gl: yes-or-no findings, never the values behind them. No fingerprint, no canvas or WebGL output, no list of fonts or plugins.
- navigator.userAgent and navigator.language, which the browser sends in the headers of every request anyway, so that the service can compare them.
- The behaviour the SDK records for every type, here on the whole page while the check runs: pointer moves and presses, measured from the widget, and counts of how the mouse moves were made, such as how many came coalesced, without movement or at an even pace. Never keys, page content or positions beyond what the behaviour check already sends.
- In the browser it stores one thing: the clearance, in localStorage under your site's origin. It goes back to WAU Captcha with auto_check answers only, never to your backend or anywhere else.
- On the service, nothing is kept beyond what the other types keep: the verdict, the score and the reason codes in the usage history of the key. Redis also counts, for an hour, the automatic passes of each address and those without a clearance, and the passes of each clearance for an hour and a day, for the limits above. The clearance itself is signed, not stored.
When to choose it
Where every extra step costs you visitors: newsletter sign-ups, comments, contact forms. For sign-ups, logins and payments, refuse the reason first_visit on your backend, or ask for an interactive type there. Choose image_distort as the fallback where people use a keyboard alone.
What it costs real people
- People on a VPN or a cloud desktop always see a puzzle: their addresses belong to cloud and hosting providers.
- Clearing your site's data, or a private window, means one more puzzle: the clearance goes with the site's data.
- So does a browser update: the clearance is tied to the browser's User-Agent.
Choosing the fallback
- Name it with data-fallback-type or fallbackChallengeType; slide_puzzle is the default. When your plan does not include the one you name, the service picks the first it does of slide_puzzle, image_distort, animal_jump and motion_noise.
- auto_check is as accessible as its fallback: most people do nothing, the rest solve the fallback. Where people use a keyboard alone, choose image_distort.
- From the fallback on, the widget behaves like one of that type until the visitor passes: a wrong answer loads another challenge of the fallback type, never auto_check again.
- Falling back is the normal path, not a sign of attack: it does not count as a wrong answer of the visitor's address, unless the answer was judged automated.
Ask for it
Name the type when you render the widget, or in the REST request:
<WauCaptcha siteKey="pk_…" baseUrl="https://api.waucaptcha.com" challengeType={ChallengeType.AUTO_CHECK} fallbackChallengeType={ChallengeType.IMAGE_DISTORT} appearance={Appearance.INTERACTION_ONLY} /><div data-wau-captcha data-site-key="pk_…" data-base-url="https://api.waucaptcha.com" data-challenge-type="auto_check" data-fallback-type="image_distort" data-appearance="interaction-only"></div>GET https://api.waucaptcha.com/challenge/new?site_key=pk_…&challenge_type=auto_check&fallback_type=image_distort- data-fallback-type and data-appearance on the element, or fallbackChallengeType and appearance on <WauCaptcha />: always (the default) shows the box from the start, interaction-only keeps the captcha hidden unless the fallback or an error must be shown.
- It always runs inline, also in MODAL mode, and starts once the box is in view. When its token expires unused, it checks again on the visitor's next click, key press or focus in the page, not by itself: every pass counts against your daily quota.
- /siteverify reports challenge_type auto_check for a visitor who passed without a puzzle, with the reason cleared or first_visit, and the fallback's type for one who solved the fallback.
In your usage charts
The success rate of auto_check is the share of visitors who passed without a puzzle. A visitor who fell back counts as answered and not solved for auto_check, and the fallback challenge counts under its own type.